



- Joined
- Jun 13, 2020
- Messages
- 6,494
- Reaction score
- 1,334
- Points
- 212
- Awards
- 2
Icebox is a Virtual Machine Introspection solution that enable you to stealthily trace and debug any process (kernel or user). It's based on project Winbagility.
Files which might be helpful:
- INSTALL.md: how to install icebox.
- BUILD.md: how to build icebox.
- fdp: Fast Debugging Protocol sources
- icebox: Icebox sourcesicebox: Icebox lib (core, os helpers, plugins...)
- icebox_cmd: Program that test several features
- samples: Bunch of examples
- winbagility: stub to connect WinDBG to FDP
- virtualbox: VirtualBox sources patched for FDP.
Some sample have been written in samples folder.
You can build them with these instructions after you installed the requirements.
If your using a Windows guest you might want to set the environement variable _NT_SYMBOL_PATH to a folder that contains your guest's pdb. Please note that icebox setup will fail if it does not find your guest's kernel's pdb.
vm_resume:
vm_resume just pause then resume your VM.
nt_writefile:Code:
cd icebox/bin/$ARCH/
./vm_resume <vm_name>
nt_writefile breaks when a process calls ntdll!NtWriteFile, and dumps what's written in a file on your host in the current directory.
heapsan:Code:
cd icebox/bin/$ARCH/
./nt_writefile <vm_name> <process_name>
heapsan breaks ntdll memory allocations from a process and add padding before & after every pointer. It is still incomplete and doesn't do any checks yet.
wireshark:Code:
cd icebox/bin/$ARCH/
./heapsan <vm_name> <process_name>
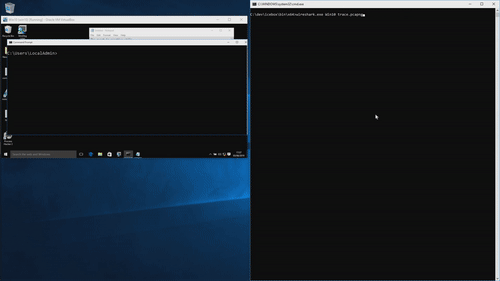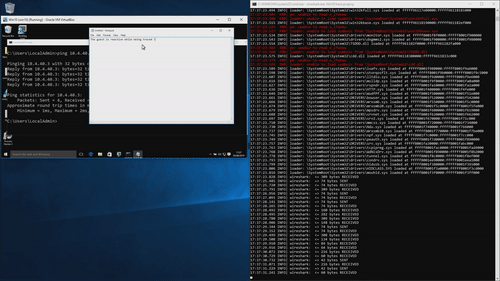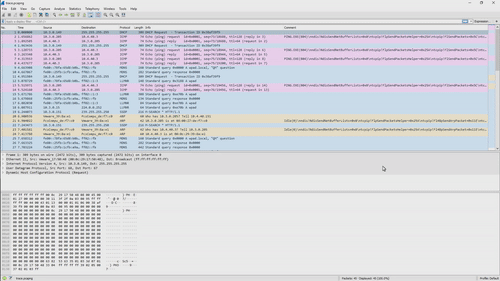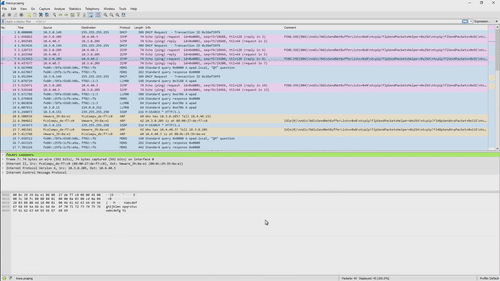
wireshark breaks when ndis driver reads or sends network packets and creates a wireshark trace (.pcapng). Each packet sent is associated to a callstack from kernel land to userland if necessary.
Code:
cd icebox/bin/$ARCH/
./wireshark <name> <path_to_capture_file>