


- Joined
- Jun 13, 2020
- Messages
- 8,148
- Reaction score
- 1,155
- Points
- 212
- Awards
- 2
The Glassworm campaign, which first emerged on the OpenVSX and Microsoft Visual Studio marketplaces in October, is now in its third wave, with 24 new packages added on the two platforms. OpenVSX and the Microsoft Visual Studio Marketplace are both extension repositories for VS Code–compatible editors, used by developers to install language support, frameworks, tooling, themes, and other productivity add-ons. The Microsoft marketplace is the official platform for Visual Studio Code, while OpenVSX is an open, vendor-neutral alternative used by editors who can't or don't use Microsoft's proprietary store. First documented by Koi Security on October 20, Glassworm is a malware that uses "invisible Unicode characters" to hide its code from review. Once developers install it in their environments, it attempts to steal GitHub, npm, and OpenVSX accounts, as well as cryptocurrency wallet data from 49 extensions. Moreover, the malware deploys a SOCKS proxy to route malicious traffic through the victim's machine and installs the HVNC client to give operators stealthy remote access. Although the initial infection was cleaned from the extension repositories, the malware returned to both sites shortly after with new extensions and publisher accounts. Prior to this, Open VSX had declared the incident fully contained, with the platform rotating compromised access tokens. The re-emergence of Glassworm was discovered by Secure Annex's researcher, John Tuckner, who reports that the package names indicate a broad targeting scope covering popular tools and developer frameworks like Flutter, Vim, Yaml, Tailwind, Svelte, React Native, and Vue.
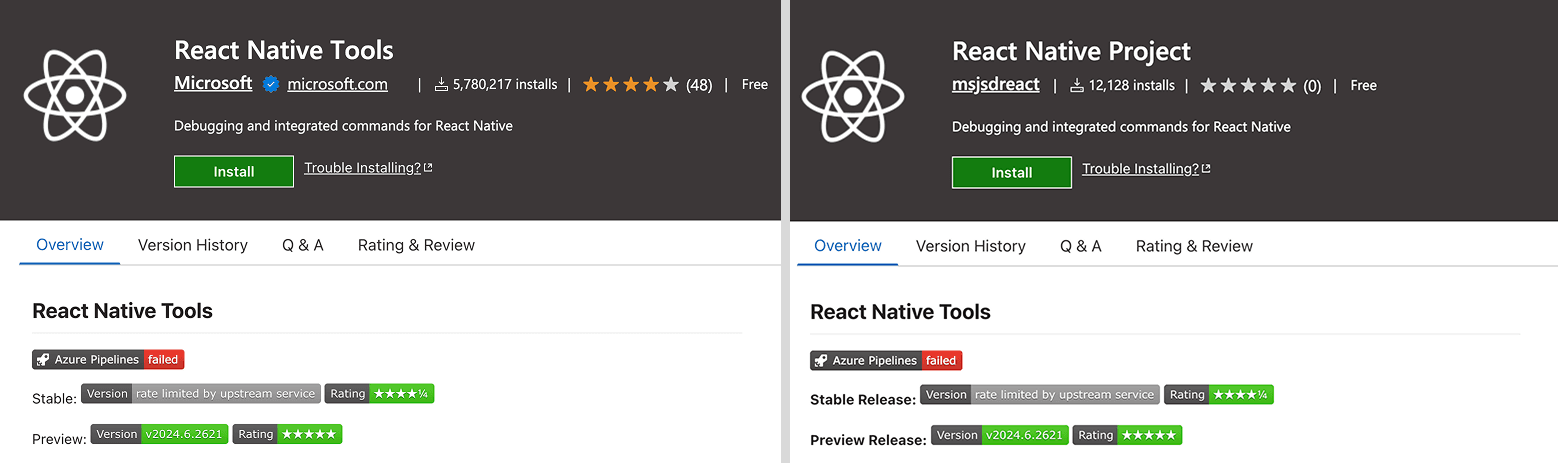
*legitimate (left) and impersonator (right) packages.
Secure Annex has now found that the third wave uses the packages listed below.
VS Marketplace
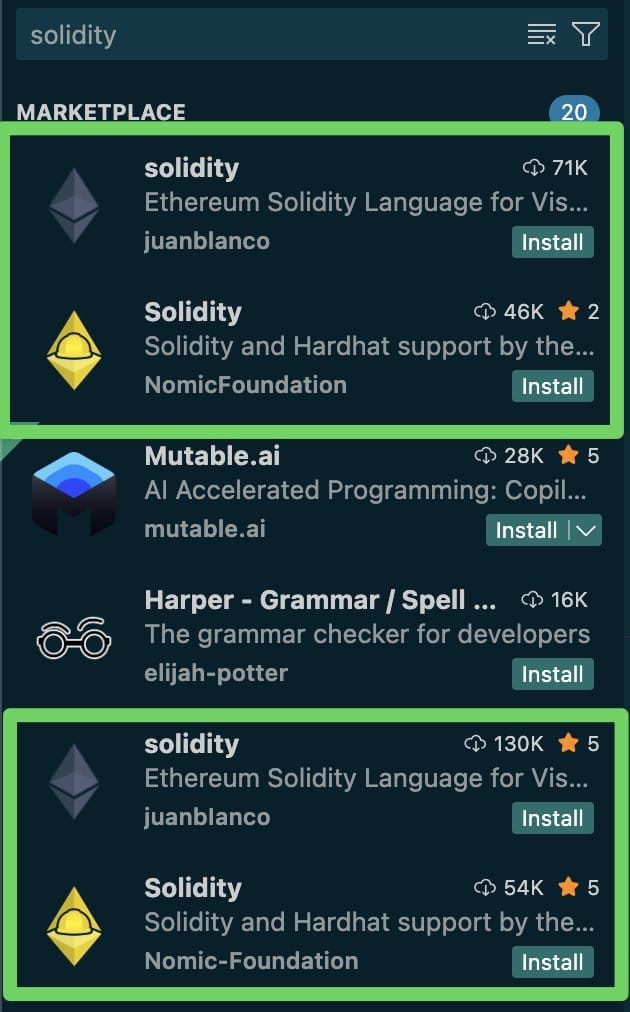
*confusing search results.
The researcher reports that Glassworm has evolved on the technical side as well, now using Rust-based implants packaged inside the extensions. The invisible Unicode trick is also still used in some cases.
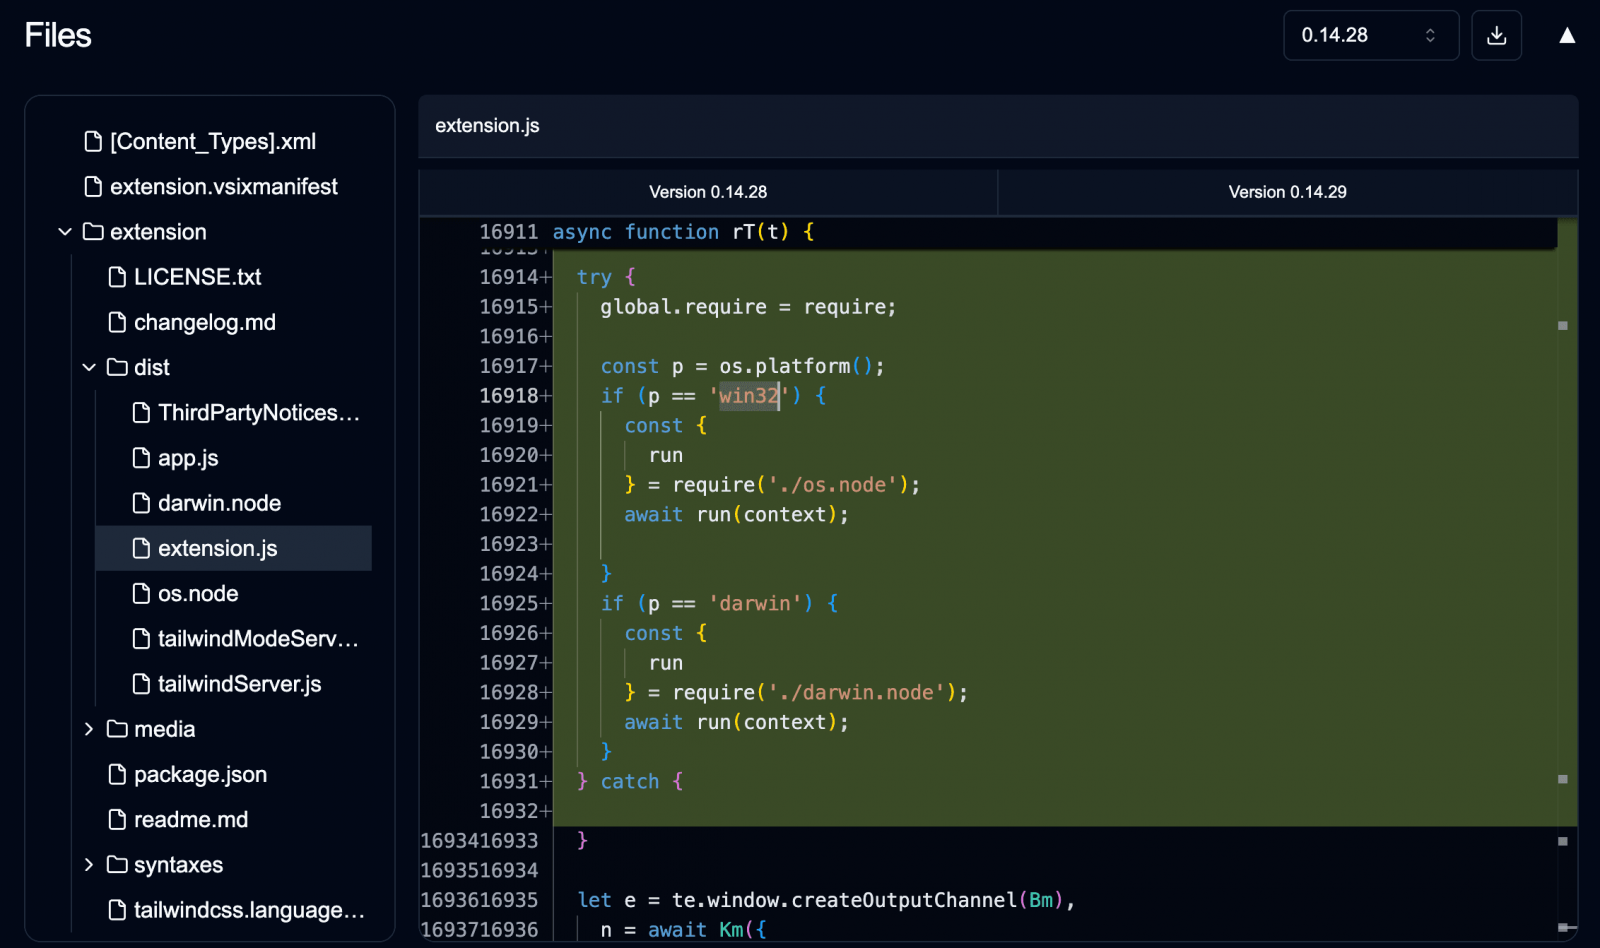
*payload.
*legitimate (left) and impersonator (right) packages.
Secure Annex has now found that the third wave uses the packages listed below.
VS Marketplace
- iconkieftwo.icon-theme-materiall
- prisma-inc.prisma-studio-assistance
- prettier-vsc.vsce-prettier
- flutcode.flutter-extension
- csvmech.csvrainbow
- codevsce.codelddb-vscode
- saoudrizvsce.claude-devsce
- clangdcode.clangd-vsce
- cweijamysq.sync-settings-vscode
- bphpburnsus.iconesvscode
- klustfix.kluster-code-verify
- vims-vsce.vscode-vim
- yamlcode.yaml-vscode-extension
- solblanco.svetle-vsce
- vsceue.volar-vscode
- redmat.vscode-quarkus-pro
- msjsdreact.react-native-vsce
- bphpburn.icons-vscode
- tailwind-nuxt.tailwindcss-for-react
- flutcode.flutter-extension
- yamlcode.yaml-vscode-extension
- saoudrizvsce.claude-dev
- saoudrizvsce.claude-devsce
- vitalik.solidity
*confusing search results.
The researcher reports that Glassworm has evolved on the technical side as well, now using Rust-based implants packaged inside the extensions. The invisible Unicode trick is also still used in some cases.
*payload.